
Trust & Compliance
AI Compliance in Australia: Governance You Can See
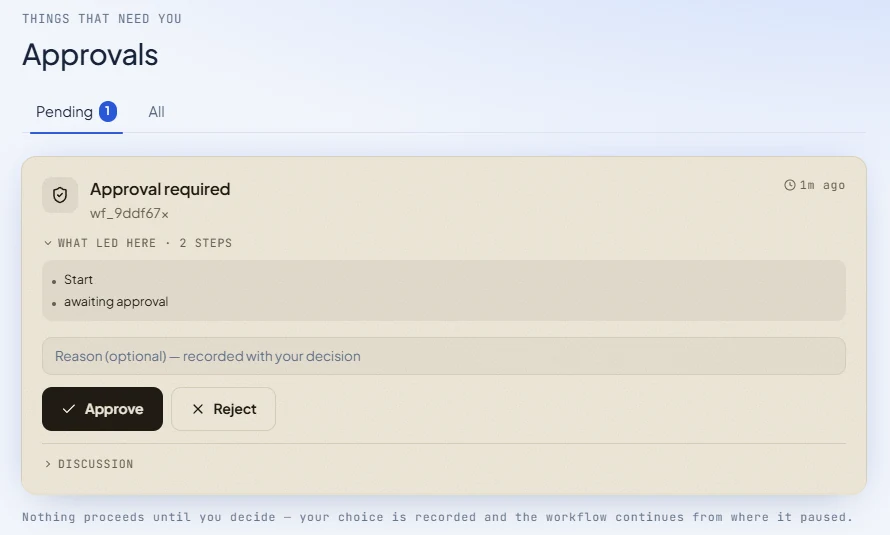
AI compliance for Australian operations rests on what a platform can show, not on what it asserts. AgentConnect pauses consequential actions for human approval, records an execution trace behind every decision, and keeps audit logs a reviewer can inspect after the fact.
- Aligned with the Privacy Act 1988, the APPs and the NDB scheme
- Runs on SOC 2-ready infrastructure
- Every consequential action can be paused for human approval
Regulated operations
Built for a Regulated World
Banking, insurance, and health-adjacent operations run under strict regulatory frameworks. Every component of the platform is built with compliance in mind, from data handling to conversation logging to access management.
For Australian operations, and accounting and finance firms handling sensitive client financial data specifically, this includes alignment with:
- The Privacy Act 1988
- The Australian Privacy Principles (APPs)
- The Notifiable Data Breaches (NDB) scheme
Built-In Governance
Secure Communication
Access Control
Controls
Governance, Demonstrated
Governance is a set of controls you can watch working, not a promise. Each of these is visible in the platform itself.
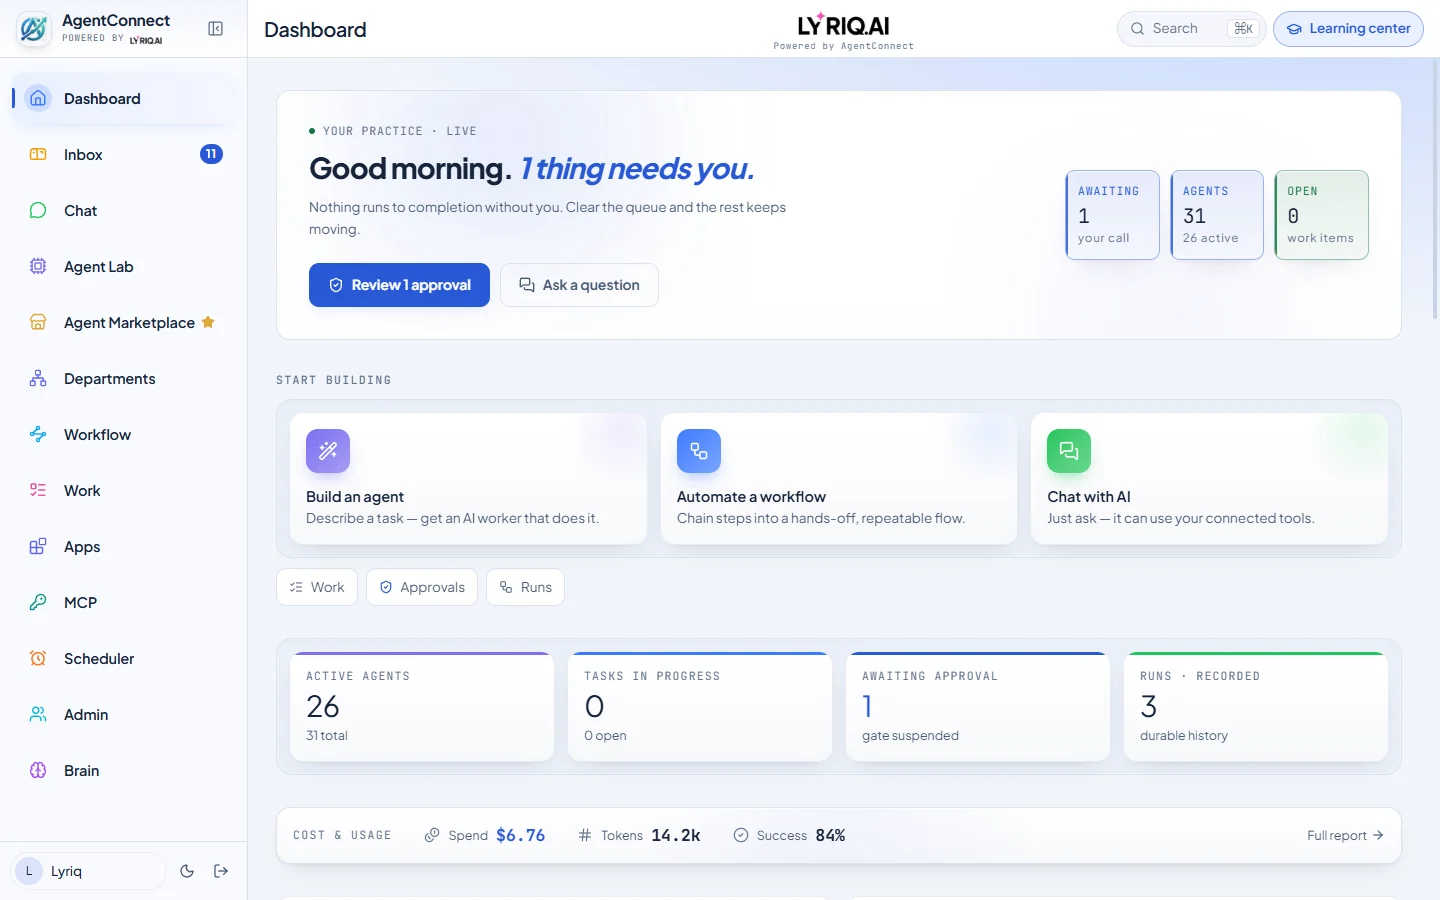
Live agent dashboard
See every agent running, which ones failed, and what each is costing, in real time.
Bottleneck visibility
When a workflow stalls, see exactly what it’s waiting on and who owns the next step.
Approval gates
Consequential actions pause for human sign-off before proceeding.
Execution traces
See exactly what led to a decision being escalated.
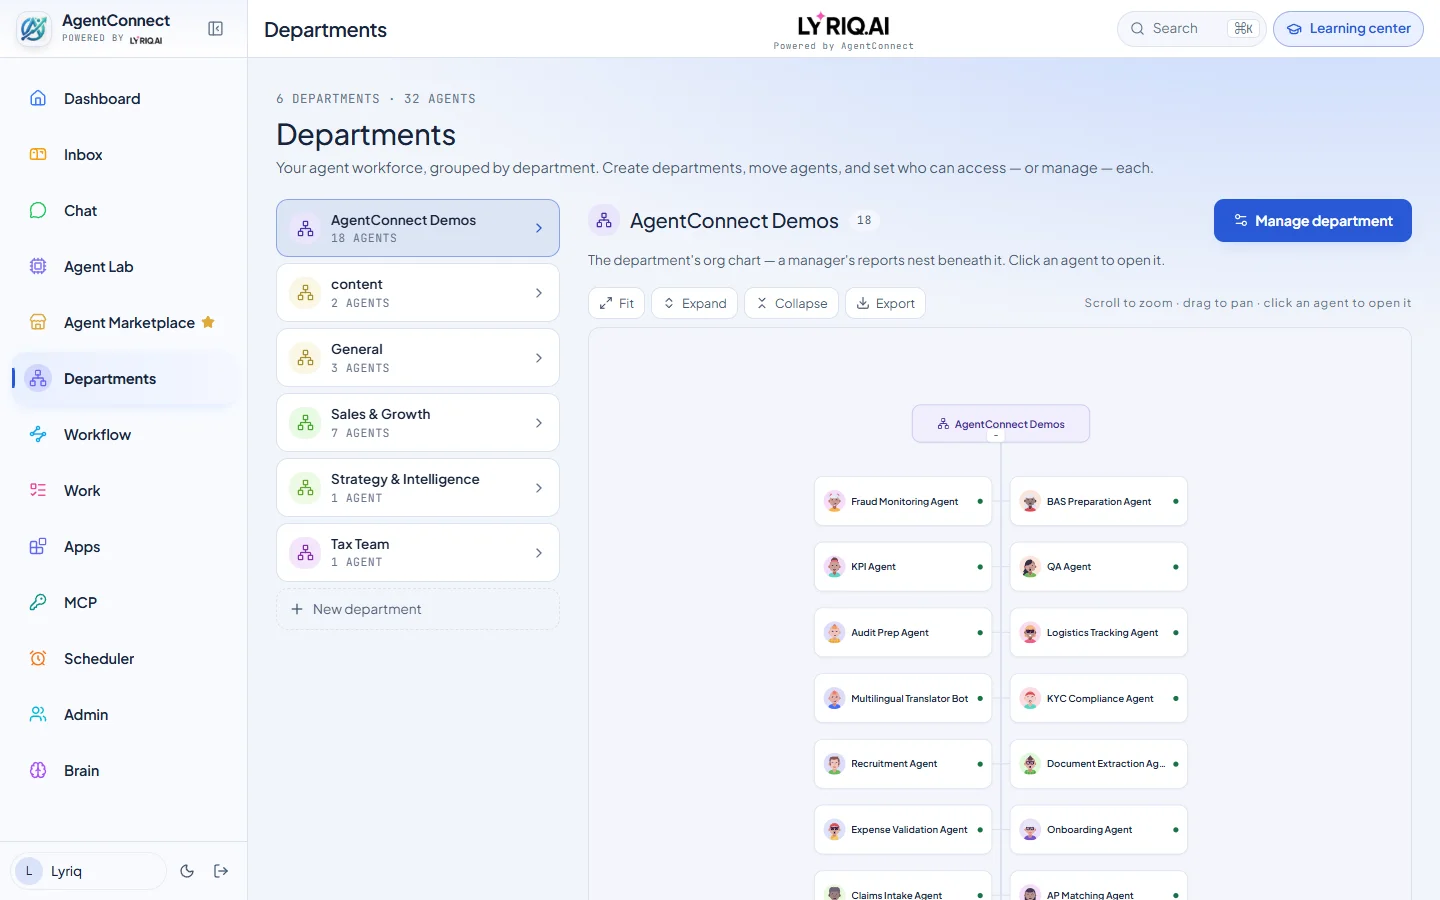
Department access controls
Structured permissions around who can access which work.
Audit and activity logs
Every action, decision, and access event is logged and traceable.
Accountability
Accountability at Every Level
Clients get visibility into compliance activity through dashboards, audit logs, and policy controls, not a claim to take on faith.
- Dedicated compliance dashboard.
- Configurable access controls.
- Automated reporting for audits and certifications.
- Third-party validation through regular security testing.
Role-based permissions, multi-factor login, and full audit logs for every access event keep control aligned to your actual policies.
Monitoring
Always Watching. Always Protected.
LYRIQ monitors system activity continuously. It detects anomalies such as irregular access, unusual API behavior, or policy violations in real time.
- Administrators receive immediate alerts, allowing quick action before issues escalate.
- Continuous infrastructure scanning.
- Alert and escalation management.
- Behavioral pattern detection.
- Live system status dashboards.
What we state, and nothing more
The Standing Compliance Line
AgentConnect runs on SOC 2-ready infrastructure. Client data is isolated per account, encrypted in transit and at rest, and deleted within 30 days of contract end. AgentConnect is model-agnostic, so no single AI provider has standing access to your data across engagements.
SOC 2-ready infrastructure is a statement about how the platform is built rather than a completed Type II audit. No other certification is claimed on this site.
Access control
Only the Right People See the Right Data
LYRIQ uses granular role-based permissions to control who can view, edit, or export data. Every action is logged, so access stays traceable across teams and systems, and aligned with security policies at all times.
- Role-based authentication.
- Multi-factor login security.
- Customizable user groups and hierarchies.
- Full audit logs for every access event.
Evidence
Proof of Compliance in Real Time
Generate audit-ready compliance reports on demand. LYRIQ tracks every interaction log, access event, and policy decision, then packages it into clean, exportable reports.
- Internal review or external audit, you have the evidence ready before anyone asks.
- Interaction and conversation logs.
- Execution traces for every agent run.
- Policy decisions and escalations.
- Compliance validation reports by region.
- System performance and uptime reports.
- Audit-ready exports, generated on demand.
- Access history and user activity.
- Sign-offs on consequential actions.
- Retention periods set per deployment.
Scale
Set Up Once. Grow Continuously.
Define your compliance framework once, and LYRIQ applies it consistently as you scale. New teams, new regions, and new channels all inherit the same standards automatically.
- 01
Consistent Enforcement
Policies apply uniformly across every agent, channel, and region, automatically.
- 02
Shared Standards
Define compliance rules once and deploy them across your entire organization.
- 03
Unlimited Portals
Create dedicated compliance views for teams, departments, or partner organizations.
- 04
Transparent Reporting
Full visibility into compliance status with exportable, audit-ready reports.
FAQ
Governance and compliance, answered
Does LYRIQ hold SOC 2 or ISO 27001 certification?
No, and we would rather say so plainly than let a badge wall imply otherwise. AgentConnect runs on SOC 2-ready infrastructure, which is a statement about how the platform is built rather than a completed Type II audit. We do not name ISO 27001, GDPR, HIPAA or any other framework on this site until there is a real, current basis for it. If a certification is a hard requirement for your procurement, tell us early so nobody wastes a cycle.
How does this work with our Australian Privacy Principles obligations?
The starting point is that your obligations stay yours. Under the Australian Privacy Principles, using a platform or disclosing personal information to a provider does not transfer accountability for it. What a platform can do is make those obligations dischargeable: data isolated per account, controls over who can access what, a record of what was accessed and when, and deletion within 30 days of contract end. Those are the mechanisms your privacy officer will actually ask about.
How does AgentConnect relate to the Essential Eight?
Honestly, less directly than vendors imply. The Essential Eight is a maturity model for your own environment, and most of it concerns endpoints, operating systems and application control that no SaaS platform participates in. Where a platform does contribute is the access side: restricting administrative privileges, controlling who can reach which work, and producing a log of it. Treat any vendor claiming to deliver an Essential Eight maturity level on your behalf with suspicion.
Where is our data stored, and who can see it?
Client data is isolated per account and encrypted in transit and at rest. AgentConnect is model-agnostic, so no single AI provider has standing access to your data across engagements. What is retained, and for how long, is set per deployment, which is a conversation worth having before contracting rather than after.
Can we see what an AI agent actually did, after the fact?
Yes, and this is the part we would rather be judged on than any certification. Every run writes an execution trace: what the agent was asked, what it read, what it decided and what it escalated. Consequential actions pause for human approval before they happen. When something goes wrong, the answer is a record rather than a recollection.
What happens to our data when the contract ends?
It is deleted within 30 days of contract end. Ask us, and any other vendor, to put the deletion window and the export format in writing at the start, when you have leverage, rather than at the end when you do not.
Your workflow, live
Bring Us Your Security Requirements
A security or compliance reviewer usually has follow-ups a standing line can't answer on its own: isolation specifics for your use case, data residency for a particular region. A call gets those answered directly.
Last updated: